Beneath the Surface: The Cloud Security Gaps Enterprise IT Teams Can No Longer Afford to Ignore
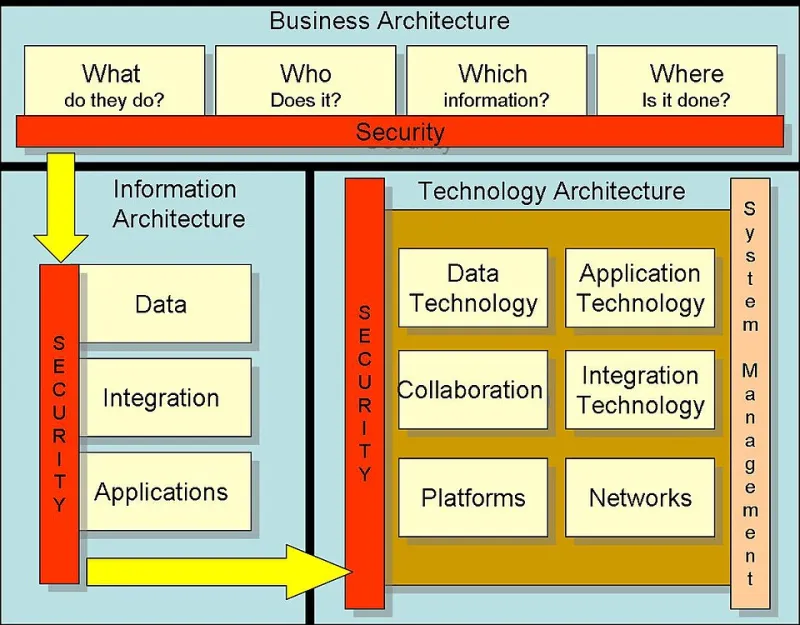
Photo: Horatio Huxham, Public domain, via Wikimedia Commons
There is a particular kind of organizational confidence that comes with moving a business to the cloud. Contracts are signed, migrations are celebrated, and productivity dashboards light up across executive briefings. What rarely makes it into those briefings, however, is the expanding attack surface that accumulates with every new cloud application added to the enterprise stack.
For IT and security leaders at US-based enterprises, 2024 has brought this tension into sharp relief. The average mid-to-large organization now operates across a dozen or more cloud-based office platforms simultaneously—document management, video conferencing, HR systems, project tracking, financial reporting. Each tool carries its own authentication model, data residency policy, and permission structure. Independently, they may be reasonably secure. In combination, without deliberate governance, they become something far more precarious.
The Invisible Architecture Problem
When enterprise teams adopt cloud tools in isolation—often driven by departmental preferences rather than centralized IT strategy—they create what security professionals sometimes call "invisible architecture." Data flows between systems through integrations that were never formally reviewed. OAuth tokens grant third-party applications broad access to sensitive directories. Shadow IT proliferates as employees connect personal productivity apps to corporate accounts without formal approval.
The consequences of this fragmentation are not theoretical. According to IBM's 2023 Cost of a Data Breach Report, organizations with high levels of security complexity faced breach costs averaging $5.28 million—significantly above the global mean. In the US, where regulatory exposure compounds financial damage, the stakes are even higher.
Consider a realistic scenario familiar to many enterprise security teams: a marketing department adopts a cloud-based content collaboration platform and, to streamline onboarding, grants all users broad read-write access to shared drives. That same drive, through a poorly scoped integration, connects to the company's CRM. A single compromised credential—obtained through a phishing campaign targeting a remote employee—now offers an attacker traversal across both systems. The breach does not begin with a sophisticated zero-day exploit. It begins with a permission setting no one thought to audit.
Compliance Pitfalls That Multiply With Every Tool Added
For enterprises operating in regulated industries, the risk calculus becomes considerably more complex. Healthcare organizations subject to HIPAA face strict requirements around where protected health information (PHI) can be stored, who can access it, and how its movement must be logged. When PHI touches even one non-compliant cloud application—perhaps a productivity tool adopted by a clinical team without IT review—the organization's entire compliance posture is compromised.
SOC 2, the auditing standard widely required by enterprise vendors and clients across sectors, introduces its own layer of complexity. SOC 2 Trust Service Criteria demand continuous monitoring, access control documentation, and demonstrable incident response capabilities. Meeting these standards across a single, well-governed platform is challenging. Meeting them across fifteen loosely integrated cloud tools, each with different logging formats and administrative consoles, is exponentially more difficult.
Many IT leaders acknowledge this reality privately but struggle to communicate its urgency to business stakeholders who see cloud adoption as progress rather than risk. The challenge is partly linguistic: "misconfigured API permissions" does not carry the same visceral weight as a breach headline. Until it does.
Where the Specific Vulnerabilities Live
Several vulnerability categories emerge consistently across enterprises with sprawling cloud office stacks.
Identity and Access Management (IAM) drift occurs when user permissions accumulate over time without regular review. An employee promoted from analyst to manager retains their original access profile while gaining new privileges—a phenomenon sometimes called permission bloat. Across dozens of platforms, this drift creates a sprawling map of excessive access that attackers are adept at exploiting.
API key exposure is a persistent problem in organizations where developers and operations teams work across multiple cloud environments. API keys stored in code repositories, shared via email, or embedded in automation scripts represent an often-underestimated attack vector. The 2023 GitGuardian State of Secrets Sprawl report found millions of valid credentials exposed in public repositories—many belonging to enterprise cloud services.
Data residency ambiguity complicates compliance for multistate and multinational enterprises. When cloud tools store data across geographically distributed servers without clear disclosure, organizations may unknowingly violate state-level privacy laws such as the California Consumer Privacy Act (CCPA), in addition to federal frameworks.
Insufficient logging and auditability means that when an incident does occur, security teams lack the forensic trail needed to understand its scope or demonstrate regulatory compliance. Fragmented platforms produce fragmented logs—stored in different formats, retained for different durations, and accessible through different interfaces.
Building a Governance Framework That Holds
Addressing these vulnerabilities does not require an enterprise to abandon the cloud tools its teams depend upon. It does require deliberate architectural thinking and consistent governance practices.
Centralize identity management. A single identity provider (IdP) with enforced multi-factor authentication should serve as the authentication backbone for every cloud application in the enterprise stack. Single sign-on (SSO) not only improves the user experience but creates a unified access control layer that IT teams can monitor and audit.
Conduct quarterly access reviews. Automated tools can flag dormant accounts, excessive permissions, and orphaned integrations. Making access review a calendar-driven discipline—rather than a reactive exercise—significantly reduces IAM drift.
Classify data before it migrates. Enterprises should establish a data classification policy that precedes cloud adoption decisions. Knowing whether a dataset contains PHI, PII, or proprietary financial information determines which cloud tools are appropriate to handle it and what contractual protections must be in place.
Require vendor security attestation. Before any new cloud tool enters the enterprise environment, IT leadership should require vendors to provide current SOC 2 Type II reports, data processing agreements, and clear documentation of their own subprocessor relationships.
Invest in unified monitoring. A security information and event management (SIEM) platform capable of ingesting logs from all cloud applications provides the visibility needed to detect anomalous behavior before it becomes a reportable incident.
The Strategic Imperative
Cloud-based office infrastructure has fundamentally reshaped how American enterprises operate, enabling distributed teams, accelerating collaboration, and reducing dependence on costly on-premises hardware. These gains are real and worth protecting.
Protecting them, however, requires IT leadership to move beyond platform adoption as a measure of progress. The organizations best positioned to leverage cloud infrastructure securely are those that treat governance not as a constraint on innovation but as its precondition. Every tool added to the enterprise stack without deliberate security review is not just a potential liability—it is a gap in the foundation upon which the entire digital operation rests.
The conversation IT leaders have not been having loudly enough is the one that begins with that acknowledgment. It is time to have it.